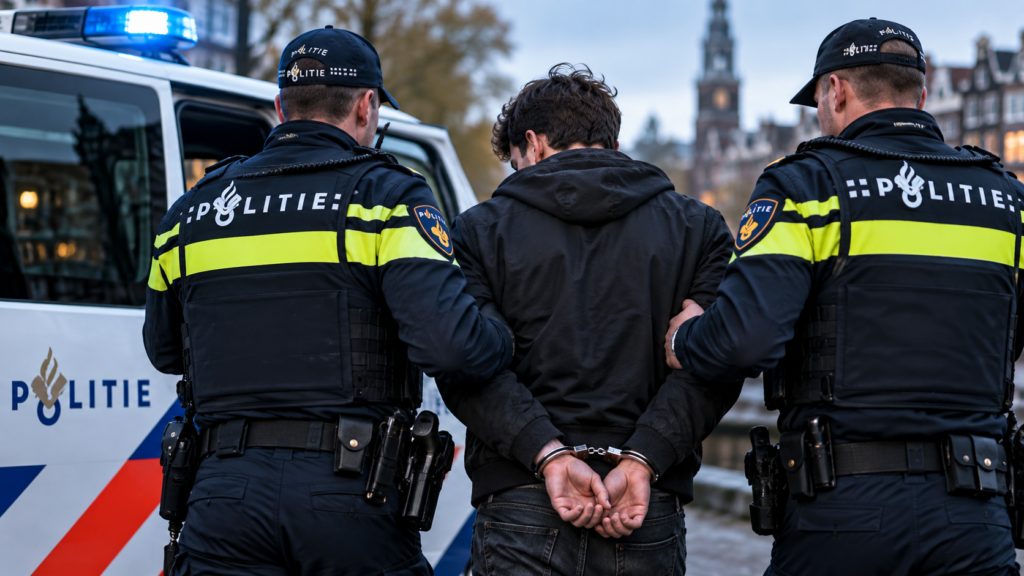
Dutch police arrested a 24-year-old in Amsterdam in their investigation into ShinyHunters, the group that claims it stole terabytes of data from the FBI’s job application site. He went to court in Rotterdam today. Almost everything else about this case is contested, including whether he has anything to do with the group.
What police have actually said
Very little, and the gap between that and the coverage is the story.
It is true that this month a 24-year-old man from Amsterdam was arrested in an investigation into the hacker group ShinyHunters.
Dutch National Police
That is the statement. Police did not name him, did not describe what he is suspected of doing, and have not detailed what was seized.
- Arrested September 15.
- Court appearance in Rotterdam District Court on September 29.
- No charges have been publicly specified.
Who reporters say he is
Independent security journalist Brian Krebs and the site DataBreaches.net identified the man as Pepijn van der Stap, known online as Umbreon. Dutch authorities have not confirmed that, and nothing here should be read as established until a court says so.
If the identification is right, it is a striking record. Van der Stap was arrested in January 2023, accused of hacking and blackmailing more than a dozen companies in the Netherlands and abroad. He pleaded guilty and was sentenced to four years, one suspended, plus three years’ probation. He was released in December 2025.
He then went to work as an offensive security lead at the Dutch firm Neo Security. Offensive security is the legitimate side of the same skill set: you are paid to break into your client’s systems and tell them how.
So the arrest came roughly nine months after his release, while he was employed in the industry.
ShinyHunters says he is not one of them
The group told CBC News that van der Stap has no connection to it, and called Dutch police unskilled and incompetent.
Treat that with the weight it deserves, which is not much in either direction. A criminal collective has obvious reasons to disown an arrested person, and equally obvious reasons to enjoy embarrassing a police force. But it is on the record, and it is the only comment from the other side of this.
ShinyHunters has spent years breaching large companies, stealing customer databases and extorting victims. It claimed responsibility for the breach of the FBI’s job application site at apply.fbijobs.gov, saying it took terabytes of material on agents and applicants. We covered that claim when it surfaced.
The BeezLoop Take
The honest state of this case is that a man was arrested two weeks ago, police have said one sentence about it, journalists have named him, and the group he is supposedly tied to says he is nobody. That is a thin factual record, and the volume of confident coverage built on top of it is out of proportion to what is known.
If the identification holds, the interesting question is not whether a hacker reoffended. It is what the security industry does with people it hires out of convictions. Offensive security firms recruit from this talent pool deliberately and mostly defensibly, because the skills are real and rehabilitation has to mean something. But the field runs on trust and access, and it has no serious equivalent of the licensing or supervision that other second-chance professions carry. A firm hiring a recently released computer criminal into a role with client system access is making a bet with somebody else’s data.
That argument can be pushed too far and we would not want it to be. Most people convicted of computer crime in their teens and early twenties do not reoffend, the industry absorbing them is better than the alternative, and an arrest is not a conviction. If this case ends in an acquittal, the people currently writing about a reformed hacker gone bad will not write the correction.
The part that should get more scrutiny than it will is the FBI breach itself. A group claimed it holds terabytes of data on federal agents and applicants, and the public accounting of what was actually taken remains vague months later. One arrest in Amsterdam does not answer that, and the arrest is getting far more coverage than the unresolved question of whose personal data is sitting on somebody’s server.
The question
If Dutch police will not say what the man is accused of doing, what is the basis for two weeks of reporting that he is a ShinyHunters operator? And whatever happens to him, where is the accounting of what was taken from the FBI?
Sources: The Hacker News · CBC News · Security Affairs · Dutch National Police